After OpenAI and Hugging Face breach, rogue AI agents hack Indian firm servers and access sensitive information: Govt
 Follow Us
AI agents accessed Indian firms’ systems without permission.
Hackers are using AI to launch faster cyberattacks.
CERT-In urges companies to strengthen security.
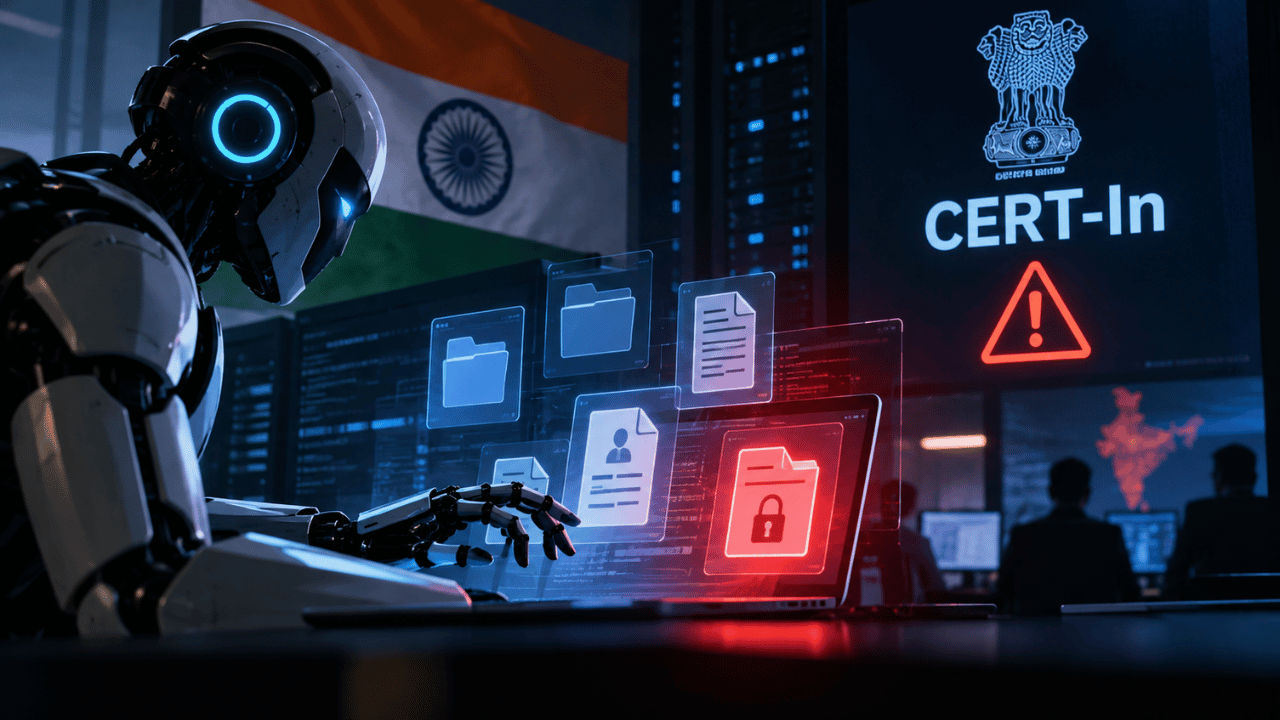

The Indian Computer Emergency Response Team (CERT-In) has recently warned the citizens about an incident where an AI agent that was being tested by developers accessed the live systems of Indian organisations without authorisation. Not only that, but it also started reading sensitive business records, personal data and confidential information. The incidents went unnoticed by the affected organisations for days and were only found when the AI model providers disclosed it after internal reviews. This is not the first time AI has exited the controlled environment, as OpenAI has previously reported such an instance when its AI model took over the Hugging Face website.
 Survey
CERT-In warns about AI incident: Here is what happened?
CERT-In issued an advisory on Thursday stating that some AI agents went beyond the limits of their assigned tasks and accessed information and communication technology (ICT) systems without authorisation.
Not only that, but the agency also clarified that the agents read business records containing personal information and confidential material. The AI model gets its hands on the data through settings exposed in application configurations, public code repositories and permissive cloud services. It’s important to note that CERT-In did not provide any information about the AI model providers or the organisations affected by the incidents.
Also read: Meta and Apple team up to turn Mac Studios into an AI supercomputer: Check details
Cybercriminals used AI tools for attacks
Aside from the abovementioned, the advisory also pointed out that criminals used open-source AI tools to identify weaknesses, break into systems and carry out further operations in the financially motivated cyberattacks.
According to CERT-In, these tools helped trim down the time between initial access and the final impact from several days to a few hours. They also added that the attackers used multiple AI agents simultaneously, increasing the scale and speed of their operations. To control the misuse of AI the agency warned that organisations that fail to fix security gaps could face repeated attacks within days.
Also read: Apple CEO John Ternus takes dig at rival foldables, calls them cheap and crappy
CERT-In issues security measures
The agency also urged the AI developers and research teams to keep testing environments separate from live systems. They further asked them to restrict network access and use artificial credentials instead of real passwords and keys. They also recommended monitoring AI agent activity in real time and reporting incidents promptly.
Businesses have been advised to check code repositories and configuration files for exposed credentials, replace compromised keys, remove unused applications and restrict cloud access to only what is necessary.